Enterprise Trust &
Runtime Governance
The Decision Control Plane for AI™ is designed for governed decisions, controlled execution, auditability, and enterprise trust.
Security here is not a compliance attachment. MuSIC™ makes trust an execution property, enforced by the same governed runtime that makes the decision.
Every decision runs inside a governed runtime.
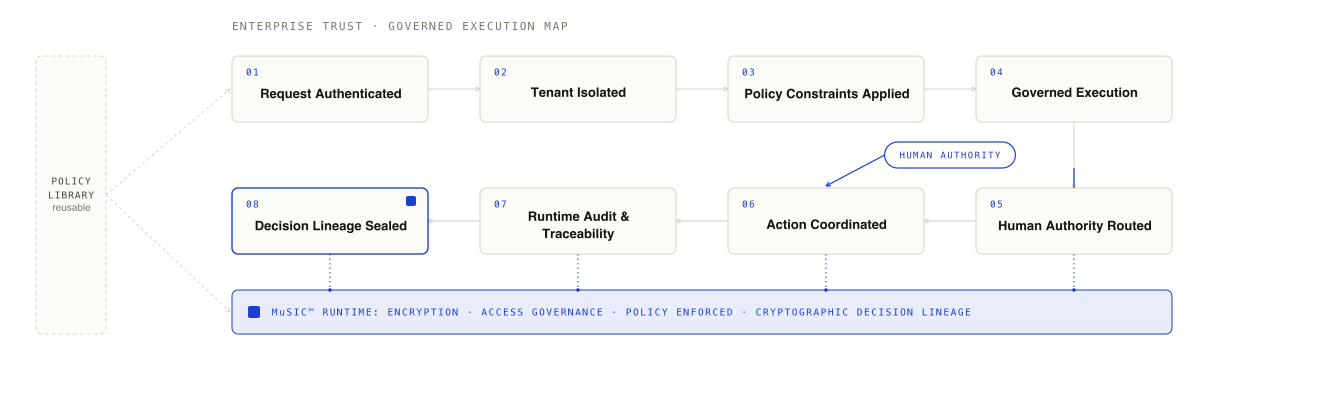
Authentication, tenant isolation, policy enforcement, human authority, audit, and lineage are not adjacent systems; they are stages of the same governed execution path.
Operational control as infrastructure: a governed runtime execution map, not a policy binder.
Runtime policy enforcement
Policy is evaluated and enforced in the runtime before any action, not documented after the fact.
Escalation governance
Escalation paths and human authority are fixed in the runtime, not improvised under pressure.
Execution controls
Every automated action runs inside bounded, policy-aware operational controls.
Reproducibility
Any decision can be reconstructed exactly as it was made: same inputs, same policy, same outcome. Model outputs are captured in the sealed record at decision time, so reconstruction reads the record rather than re-running a nondeterministic model.
Every decision, sealed to a verifiable record.
MuSIC seals each governed decision with cryptographic decision lineage: a tamper-evident runtime record of what was decided, on what inputs, under which policy.
This is operational reproducibility and governed auditability, built so review operates on the runtime record itself, not a reconstructed narrative.
Tamper-evident records
Every decision is sealed to a verifiable, tamper-evident runtime record.
Execution traceability
Captured at runtime: what was decided, on which inputs, under which policy, and by whose authority.
Operational reproducibility
Lineage supports faithful reconstruction and review of any governed decision.
Governed auditability
Audit and review operate on the runtime record, not reconstructed narratives.
Curated controls, operating today.
Tenant isolation
Strict per-tenant data and execution isolation across the platform.
Encryption
Data encrypted in transit and at rest with managed key handling.
Authentication & access
Enterprise SSO, role-based access, and least-privilege operational access governance.
Runtime safeguards
Bounded execution, policy gates, and approval thresholds enforced at the runtime.
Transparent by default.
Our SOC 2 control set is implemented and an independent audit is in progress. We state exactly where we are.
Our SOC 2 control set is implemented, and an independent audit is in progress.
Aligned to NIST AI RMF principles: runtime governance, policy enforcement, and decision lineage follow the framework for governed AI operation.
Tenant isolation, encryption in transit and at rest, and least-privilege access governance are enforced today.
SynergyPartners.ai does not claim attestations or certifications it has not completed. We will publish attestation status as it is formally issued.
Trust isn’t documented.
It’s executed.
The platform governs AI-driven decisions without sacrificing enterprise control: governance enforced where the decision is made.
Trust is an execution property
Security here is not a document set; it is enforced by the same runtime that executes the decision.
Governance scales with execution
Policy propagates centrally; controls hold identically as operations scale across the enterprise.
Auditability is built in
Every governed decision is reproducible and reviewable by construction, not by reconstruction.
Review the runtime governance posture with our team.
A working session for CISOs, CIOs, and security leadership: the runtime execution model, decision lineage, tenant isolation, and current attestation status, in detail.
For CISOs, CIOs, heads of security architecture, and enterprise risk leadership.